
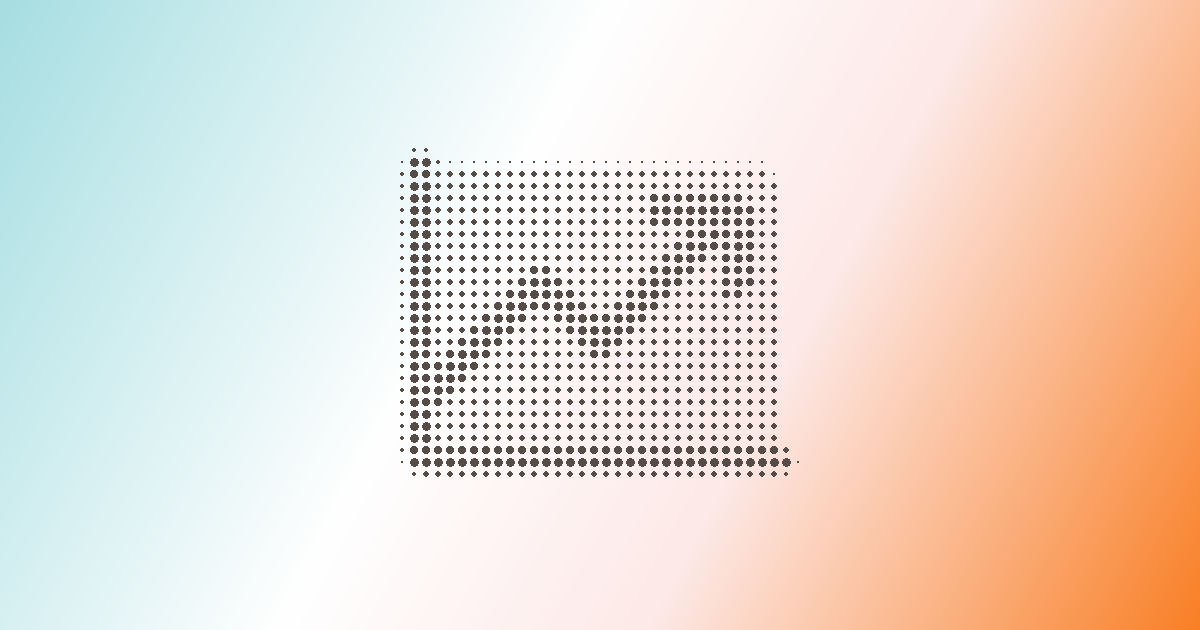
Our chart this week counts the software security flaws given a CVE (Common Vulnerabilities and Exposures) number each year since the system began in 1999. A CVE is the public record that suppliers and security teams use to track a flaw and its fix. From 2005 to 2016 the count stayed between about 4,000 and 8,000 a year, then climbed steadily to just under 48,000 in 2025.
2026 has broken that pattern. 85,333 records have been published so far, more than double the same point last year. The weekly rate rose from about 1,400 in the first half of the year to about 3,000 from July, and the week of 12 October set a record of 5,460. At that rate the year will end close to 120,000.
Google's threat intelligence group found monthly disclosures doubled between January and July, and IBM X-Force counted an almost sevenfold rise for Microsoft, Oracle, Google Chrome and Apache. Neither can prove the cause, but both point to AI tools finding flaws at a scale human researchers cannot match. Google found the flaws it could trace to AI were also more serious: half let an attacker run their own code, against about a quarter of all CVEs.
Only a small share are used in attacks. CISA has added 270 flaws to its list of those known to be exploited this year, against 85,000 new records. And in April NIST said it could not clear its backlog of records awaiting analysis, so many now arrive without a severity score. Keeping up is a matter of filtering:
- Know what you run. Keep a current list of your software and versions, including open-source packages, so a new advisory can be matched in minutes.
- Act on what attackers are using. New entries on CISA's exploited list come first, and deserve a fix within days.
- Rank the rest by likelihood. A severity score says how bad a flaw could be; EPSS estimates how likely it is to be exploited in the next month.
- Don't wait for NIST. Where its analysis has not arrived, use the supplier's own rating or the score CISA adds to many records.
- Follow your suppliers. Subscribe to security notices for internet-facing systems such as firewalls, VPNs and email servers, which are frequent targets.
- Automate the matching. A scheduled script or scanner can compare these feeds with your software list each day and alert only on matches.
Sources to follow
Official lists, data sources and news sites that track new flaws as they appear
Official
CISA Known Exploited VulnerabilitiesFlaws confirmed as used by attackers, with deadlines for US agencies to fix them. The clearest list of what to patch first.
cisa.gov
Official
CISA advisoriesWarnings about active attack campaigns, with the steps organisations should take.
cisa.gov
Data
NVD dashboardNew CVEs received this week, month and year, and how many are still waiting for analysis.
nvd.nist.gov
Data
FIRST EPSSA daily estimate of how likely each CVE is to be exploited in the next 30 days.
first.org
Data
OSVChecks whether a specific version of an open-source package is affected, and which version fixes it.
osv.dev
Data
GitHub Advisory DatabaseAdvisories for open-source packages, including flaws that never receive a CVE number.
github.com
News
BleepingComputerFast reporting on breaches and attacks, often with the affected company's own statement.
bleepingcomputer.com
News
The Hacker NewsDaily coverage of newly disclosed flaws and the campaigns exploiting them.
thehackernews.com